
Security model
What we protect, how we protect it, and what we deliberately do not do.
Threat model first
Email security is often marketed as a feeling. We prefer to be specific. ITProMail is designed to defend against passive network observers, opportunistic attackers, credential stuffing, phishing of our members, and the loss or theft of storage hardware.
It is not designed to protect against a compromised device, a coerced recipient or metadata visible to other mail servers. No hosted email provider can honestly claim otherwise. For content that must stay secret from everyone including us, use end-to-end encryption.
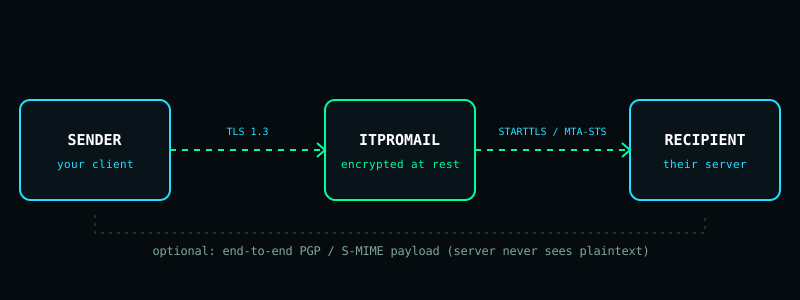
Defense in depth
Storage
Mailboxes are encrypted at rest. Backups are encrypted separately and retained for a limited period, then destroyed.
Transport
TLS 1.2 minimum with TLS 1.3 preferred, modern cipher suites only, HSTS on all web properties and MTA-STS for hosted domains.
Authentication
Passwords are hashed with a memory-hard function. TOTP and FIDO2 are supported, and IMAP/SMTP use revocable app passwords.
Privacy
Webmail loads no third-party scripts, blocks remote images by default and strips common tracking parameters from links.
Infrastructure
Minimal exposed services, key-only administrative access and short log retention limited to what is needed to run the service.
Anti-abuse
Outbound rate limits and reputation monitoring protect the deliverability of every member sharing our IP space.
Deliberate omissions
No ad profiling
Message content is never used for advertising, scoring or analytics.
No third-party trackers
No analytics beacons, social widgets or ad networks on our sites or in webmail.
No data sales
We do not sell, rent or trade member data. Our revenue is subscription fees.
Vulnerability disclosure
If you believe you have found a security issue affecting ITProMail, please email security@itpromail.com. Encrypt sensitive reports to the key published at our Web Key Directory endpoint where possible.
- Give us a reasonable window to investigate and fix before public disclosure.
- Do not access, modify or destroy data that is not your own.
- No denial-of-service testing or social engineering of staff or members.
Good-faith research that follows these rules will not be met with legal action. Our security.txt is kept current.